BMW hackers rewarded for flagging security flaws
Security company uncovers vulnerabilities in several BMW models, enabling the marque to issue software patches
A team of ‘white hat’ hackers has uncovered 14 software and hardware vulnerabilities in a range of BMWs after carrying out what BMW says is the “most comprehensive and complex testing ever conducted” by a third-party company.
The hackers found a range of vulnerabilities in the BMW i3 and X1, as well as the previous-generation 5 Series and 7 Series. Eight of the flaws related to the cars’ infotainment systems, four were linked to their telematics units, and two concerned the vehicles’ on-board diagnostics’ gateway.
• Car security: staying one step ahead of criminals
The Chinese cyber-security firm that uncovered the flaws, Tencent Keen Security Lab, said “these attack chains could be utilized by skilled attackers at a very low cost”, adding they would allow hackers to “trigger or control car functions over a wide-range distance”.
While nine of the attacks required a physical connection to be made between the cars and hacking equipment, five could be enacted remotely by exploiting weak points in Bluetooth and GSM connections, as well as BMW’s ConnectedDrive infotainment services.
After a year’s worth of research uncovering the flaws, Tencent Keen Security Lab alerted BMW to the vulnerabilities. The carmaker confirmed Tencent’s findings within two weeks, and subsequently announced it had addressed the vulnerabilities with “upgrades [that] were rolled out in the BMW Group backend and uploaded to the telematics control units via over the air connection.”
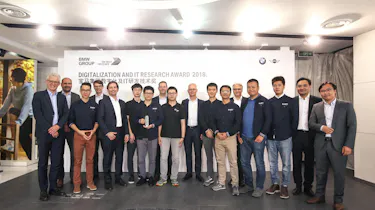
BMW was so impressed with the Tencent’s discoveries - calling its endeavours “outstanding research work” - that it awarded the company the first-ever BMW Group Digitalization and IT Research Award. The two firms are now “discussing options for joint in-depth research and development activities.”
• How to avoid keyless car theft
BMW’s decision to reward and plan future projects with Tencent Keen echoes similar programmes employed by Silicon Valley tech companies. Facebook has paid out $6.3 million (approx £4.7 million) to white hat hackers for pointing out vulnerabilities since 2011, while Google has awarded $12 million (approx £9 million) since 2010.
With internet-connected cars becoming increasingly standard within the marketplace, and huge investment in autonomous cars from industry, manufacturers may turn to white hat hackers to unearth security flaws more frequently in the future. This practice could act as a safety net for vulnerable software, enabling weaknesses to be patched before being exploited.
Protect yourself against keyless car theft with these Faraday car key signal blockers…